

Do you need to document your information security practices for customers, partners, regulatory authorities, or in response to a request for proposals?
With MasterQMS, you can consolidate documentation, risk assessments, controls, tasks, audits, and improvements in one place, giving you a clear overview, helping you assign responsibilities, and preparing you for ISO 27001 certification.
MasterQMS helps companies achieve ISO 27001 certification by making the documentation process easier and more manageable.
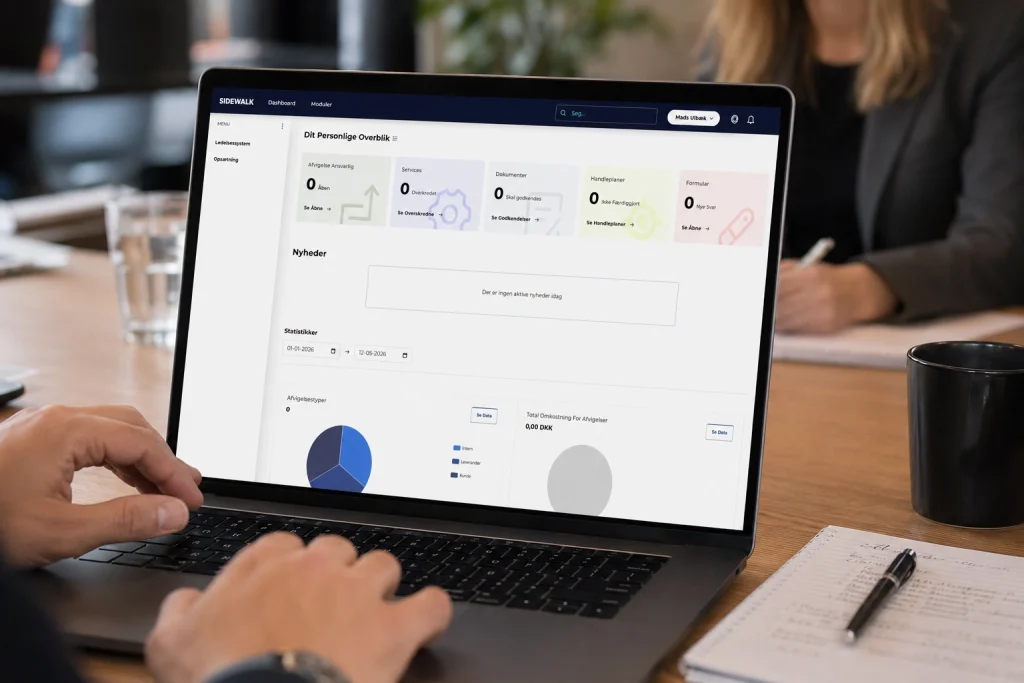
In our management system, you can gather all necessary documentation in one place, get an overview of any gaps, track status, and communicate with colleagues. In addition, we offer advice and consulting services if you need guidance.
An ISO 27001 standard is an international standard for management systems for information security. The standard sets out the requirements for a system that helps companies protect sensitive information, reduce risks and ensure a structured approach to information security.
The information security management system according to ISO 27001 enables companies to:
Make the path to ISO 27001 certification more manageable and action-oriented. Many people find information security to be complex and documentation-heavy, but at MasterQMS, we translate the standard’s requirements into concrete processes that can be used in your day-to-day operations. Achieving certification requires a structured information security management system. With our digital platform, we consolidate policies, risks, controls, incidents, and documentation in one place, making it easy to implement and comply with the standard’s core requirements in practice:
The organization must develop an information security policy, designate responsible roles, and ensure clear management commitment.
Risk assessments must be conducted to systematically identify, evaluate, and manage threats and vulnerabilities.
The organization must document relevant security controls in a Statement of Applicability (SoA) and ensure that the requirements can be met.
There must be processes in place for incident management, internal audits, and continuous improvement of information security.
A simple and structured process from overview to a fully implemented system.
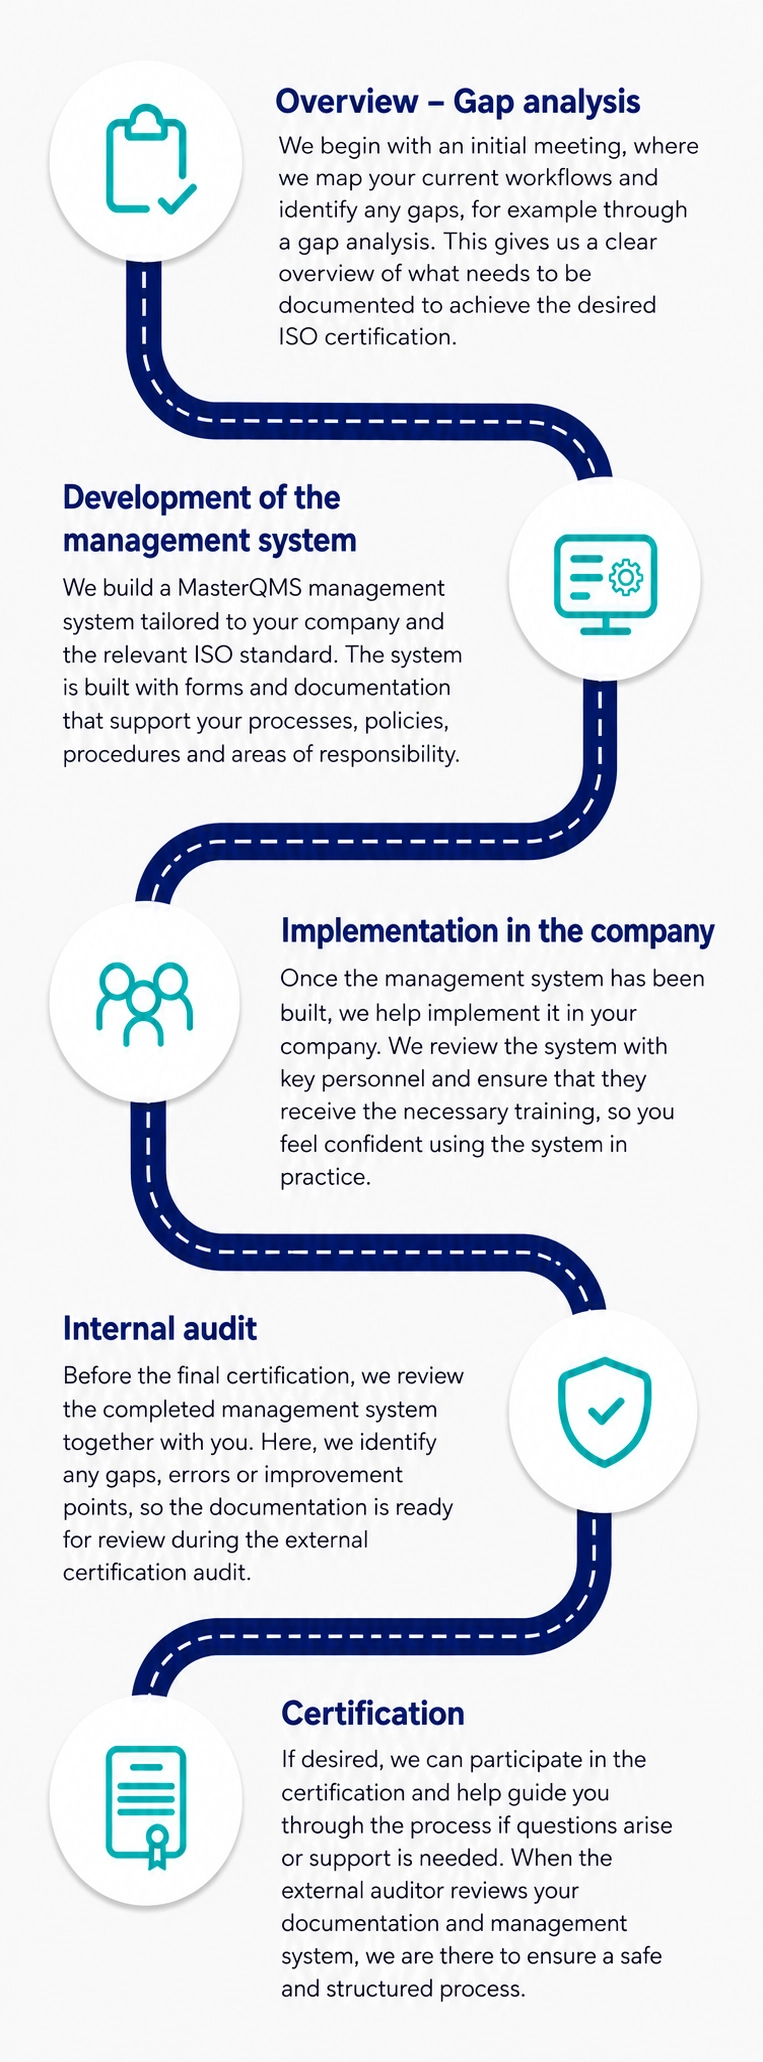
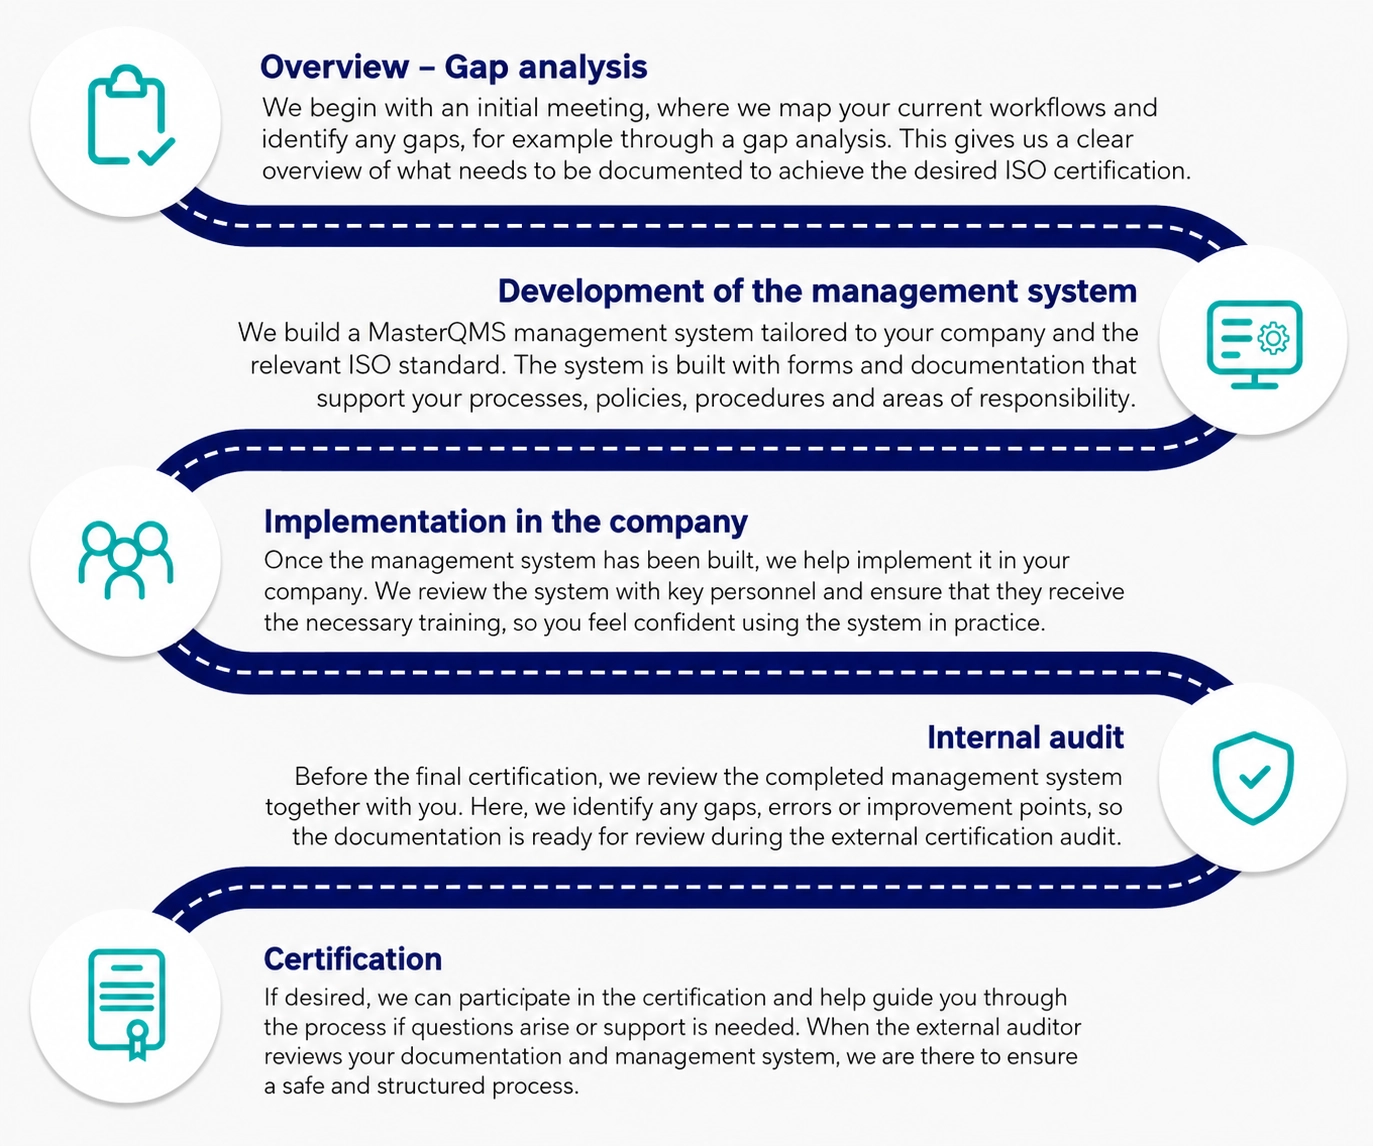
The path to ISO 27001 certification starts with building a management system for information security that meets the requirements of the standard. The system must be implemented, documented and finally reviewed by a certification body.
At MasterQMS we assist you through the entire process:
We make sure that you are ready for certification – safely and securely.
At MasterQMS, we offer flexible solutions so you can choose the approach that best suits your resources and needs:
Try our system FREE for 30 days and see how it can add value to your business.
All solutions are scalable and can be easily combined with other standards, such as ISO 9001.
Are you ready to strengthen the company’s information security?
Information security is not just about technology – it is about structure, responsibility and culture. With ISO 27001 you get:
Regardless of whether you are a small IT company, a SaaS platform or a large healthcare organisation, MasterQMS can help you ensure that your company meets all requirements of ISO 27001.
Information security is about protecting a company’s information from unauthorized access, loss, or misuse. It encompasses digital data, physical documents, and the knowledge held by employees and stored in the company’s systems. The purpose of information security is to ensure the confidentiality, integrity, and availability of information so that a company’s data is protected against cyberattacks, human error, and technical failures.
Information security is crucial for businesses because they are increasingly handling large volumes of data, including customer data, business-critical information, and internal documents. If this information is compromised, it can lead to financial losses, a loss of trust among customers and business partners, and potential legal consequences. By taking a systematic approach to information security, businesses can reduce the risk of data breaches, strengthen their resilience against cyber threats, and provide greater peace of mind for customers and stakeholders.
ISO 27001 is an international standard for information security. The standard outlines the requirements for establishing, implementing, and maintaining an information security management system, also known as an ISMS. The purpose of ISO 27001 is to help organizations identify risks to their information and implement appropriate security measures. The standard can be used by organizations of all sizes and in all industries and is globally recognized as a framework for effective information security management.
ISO 27001 certification is official confirmation that a company meets the requirements of the ISO 27001 standard. The certification is issued by an independent certification body following a thorough audit of the company’s information security management system. The certification demonstrates that the company takes a structured approach to protecting its information and managing risks related to data security.
The cost of ISO 27001 certification depends on several factors, including the company’s size, the complexity of its IT systems, and how far the company has already progressed in its information security efforts. Costs may include establishing the information security management system, any consulting services, employee training, and the certification audit itself. In addition, there will typically be ongoing costs for surveillance audits to maintain the certification.
To obtain ISO 27001 certification, the company must establish and implement an information security management system in accordance with the standard’s requirements. This involves, among other things, identifying information assets, analyzing security risks, and implementing relevant security controls. Once the system is implemented and functioning in practice, an accredited certification body conducts an audit of the company. If the company meets the requirements of the standard, certification can be issued.
Being ISO 27001 certified means that the company works systematically to protect its information and manage risks related to data security. The certification demonstrates that the organization has implemented an information security management system that meets international standards. It signals to customers, business partners, and regulatory authorities that the company takes information security seriously and is committed to continuously improving its security processes.
An ISO 27001 certification is typically valid for three years. During this period, annual follow-up audits are conducted to ensure that the company continues to meet the requirements of the standard. When the certification period expires, the company must undergo a new certification process to maintain its certification.
ISO 27001 is used by companies and organizations worldwide and is one of the most widely adopted standards in the field of information security. The standard is used by small businesses, larger organizations, and international corporations alike that seek a structured approach to protecting their data and managing security risks.
Implementing ISO 27001 can help companies protect sensitive information and reduce the risk of data breaches and cyberattacks. The standard establishes a structured approach to information security and contributes to better risk management and internal processes. At the same time, ISO 27001 certification can strengthen a company’s credibility with customers and business partners, as it demonstrates that the company takes a systematic approach to data security and information protection.
You should implement ISO 27001 because the standard helps an organization protect its information systematically. It provides a structured approach to risk management, enabling the organization to identify security threats, reduce vulnerabilities, and ensure the confidentiality, integrity, and availability of data. At the same time, ISO 27001 can strengthen the trust of customers and business partners because the organization demonstrates that it takes a professional approach to information security. Implementation can also make it easier to comply with legal requirements, contractual obligations, and internal security policies.
Are you ready to take the next step?
Fill out the form, and let’s talk about how our system can help your business thrive.
We demonstrate how our system creates value in your business — whether you want to implement certifications or document your processes to ensure effective governance.
Try our system FREE for 30 days and see how it can create value for your business.